Blog
[searchandfilter id="480"]
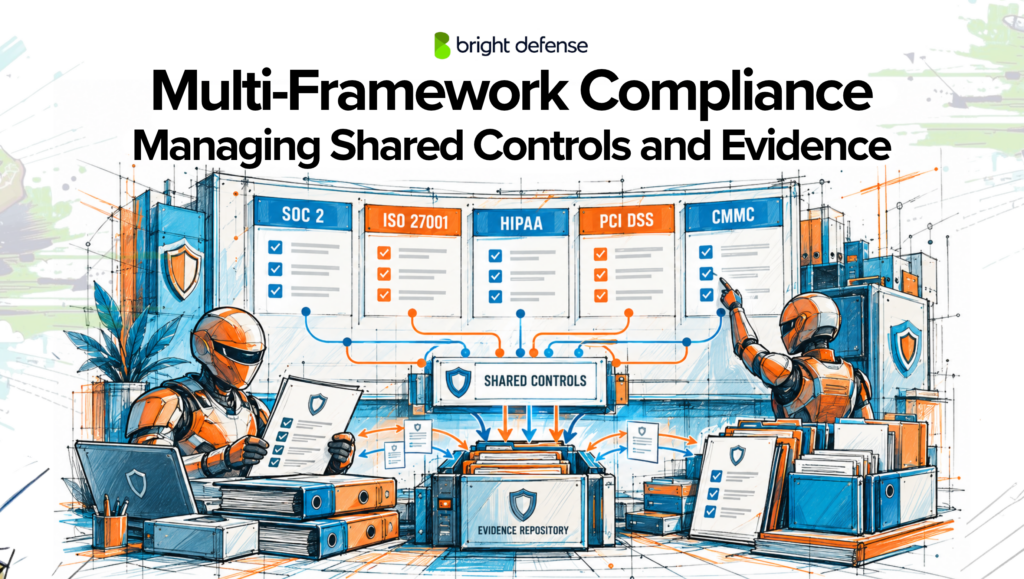
Multi-Framework Compliance: Managing Shared Controls and Evidence
Multiframework compliance brings the requirements of multiple standards and regulations into one…
SOC 2 Policies And Procedures
SOC 2 policies explain how your organization protects information and who is…
5 Best MDM Softwares for Getting Compliance Fast in 2027
Every major security framework eventually asks the same question about your laptops…
SOC 2 Password Requirements for 2026
SOC 2 password requirements are the authentication controls an organization uses to…
ISO 27001 vs SOC 2 – Whats the Difference
ISO 27001 and SOC 2 help organizations demonstrate their security practices, but…
50+ CMMC Statistics for 2026
Defense contractors need more than a signed contract to keep Department of…
60 SOC 2 Compliance Statistics for 2026
About 70% of Drata customers hold a SOC 2 attestation, according to…
What Is The Difference Between DoS Attacks And DDoS Attacks?
A denial-of-service (DoS) attack makes a service unavailable by overwhelming or disrupting…
HIPAA Backup and Recovery Requirements for 2026
Only 51% of healthcare organizations hit by ransomware in 2025 used backups…
Get In Touch